methods / how-to-unblock-any-website
How to unblock any website: the diagnosis ladder
Short answer
Find the layer the block lives at - DNS, connection, IP or on the site itself - then match the fix: encrypted DNS for name filtering, ECH or a tunnel for connection cuts, a different exit for IP and geo blocks, an archive copy when nothing else is allowed.
Most people search for one magic trick. There isn't one - there is a diagnosis. A website block is a deliberate failure somewhere between your device and the page you want, and it always happens at a specific layer: the name lookup (DNS), the connection setup (TCP and the TLS handshake), the raw route to the server (IP), or on the site itself (geo and account walls). Each layer has one fix that works and a dozen fixes that waste your time [1].
This guide gives you the diagnosis routine first, then a method menu matched to what you found. Every method has a full guide on this site; this page is the map. We keep it updated as blocking behavior changes - the measurement data we cite comes from OONI, a non-profit that has collected billions of open censorship measurements from volunteers worldwide since 2012 [1][4].
The five-minute first-aid routine
Do these steps in order. They resolve the majority of everyday blocks, and if they don't, they tell you exactly which of the deeper guides you need:
- Confirm the site itself is up: open it on mobile data instead of Wi-Fi. If it loads there, the site is fine and your network is doing the blocking - skip to the diagnosis section below.
- If you see a search page, an ISP notice, or "server not found" instead of the site, change your DNS resolver to 8.8.8.8 or 1.1.1.1, or switch on encrypted DNS (DoH) in your browser. Full steps: change your resolver or DoH setup [8].
- If the page hangs forever and only on
https://, your connection handshake is being cut. Try Cloudflare WARP (free, one toggle) or turn on ECH in your browser [2]. - If nothing to that site connects at all, or every page on the domain is dead, you need a tunnel with a new exit: WARP, Psiphon or the Tor Browser.
- If the site loads but refuses you (region, age gate, account wall), the block is on the site itself - you need an exit in an allowed country, which means a VPN or another network path.
- Can't install anything at all? Read the site from an archived copy or a translate proxy - both need zero setup.
- Verify what actually happened with OONI Probe [5], then check the public measurement history of the site in OONI Explorer [4].
Diagnose: which layer ate the site
Blocking is invisible only if you skip the diagnosis. The symptoms you see in the browser map tightly onto the layer where the interference happens. OONI's Web Connectivity test - the open-source measurement standard used worldwide - distinguishes exactly these kinds: DNS tampering, TCP/IP blocking, and blocking at the HTTP layer [1].
| What you see | What it means | Fix that works |
|---|---|---|
| Block page, ISP notice, "server not found", NXDOMAIN | Your resolver answered with a lie or the filter list kicked in | Different resolver, ideally encrypted DNS [1][8] |
Page hangs forever, only on https:// | The TLS handshake is cut; the site name inside the handshake (SNI) is often the trigger [6] | ECH, WARP, Tor, Psiphon, VPN [2] |
| Nothing to that address connects | IP-level block: packets to the server address are dropped | Any tunnel with a different exit |
| Site loads, then refuses you (region, age, account) | The block is on the site itself, not your network | Exit in an allowed country |
| Whole site family dead, domain and mirrors both | Registry- or ISP-level filtering, often DNS plus IP | Tunnel (WARP, Psiphon, Tor) [1] |
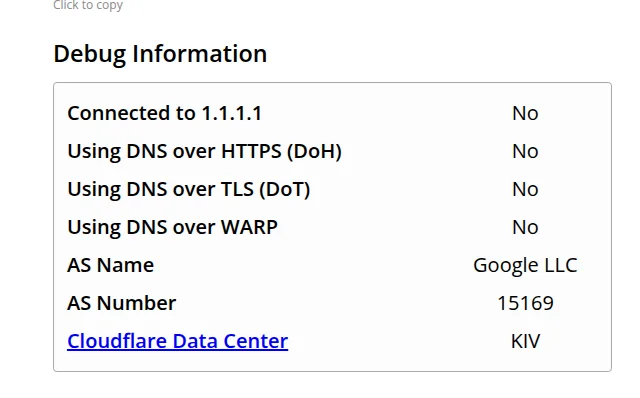
The Cloudflare 1.1.1.1 help page is a quick self-test you can run in the browser: it shows whether your DNS traffic is actually using an encrypted resolver or WARP right now, and what network you are on [7].
You can also measure the block directly. OONI Probe runs the same test sequence an expert would run - resolver identification, DNS lookup, TCP connect, HTTP request - and compares the results between your network and a control server. If the answers differ, you have proof of interference and of which kind [1].
The four layers a block can live at
Every site block on the internet lives at one of four layers, and the fix follows the layer:
- DNS layer. Your resolver is asked "where is this site?" and answers with nothing, a wrong address, or a block page. This is the most common casual block because it is cheap and easy to filter - and it is also the most completely beaten fix: an encrypted resolver in your browser or OS sidesteps the entire question [1][8].
- Connection layer. Your resolver answered correctly, but the handshake to the server is cut. Modern censorship inspects the TLS handshake, where the plaintext SNI field still announces which site you are visiting - so the censor can cut exactly the blocked domains and nothing else [6]. The protocol-level answer to this is ECH, which encrypts the whole ClientHello including SNI [2]; the practical answers are tunnels that hide the handshake entirely.
- IP layer. Packets toward the server's address are dropped. Nothing you do in DNS matters; you need to send your traffic to a different exit point that can still reach the server [1].
- On the site. The page loads fine, then the operator refuses your country, your datacenter's IP range, or an unverified account. No network trick changes the operator's mind - only a different exit country does.
Match the symptom to the layer, then pick the fix:
The method menu
Every method below is free unless marked. The honest rule: pick the lightest tool that solves your diagnosed layer, and prefer nonprofit or open-source tools for anything that touches credentials.
| Method | Beats | Fails against | Cost |
|---|---|---|---|
| Resolver change / encrypted DNS | DNS blocks, filter lists | SNI cuts, IP blocks, geo walls | free, minutes |
| ECH in the browser | SNI-based cuts on supporting hosts | hosts without ECH, IP and geo blocks | free |
| Cloudflare WARP | DNS blocks plus SNI filtering | hardened DPI, geo walls | free |
| Psiphon / Lantern | mixed DPI and filtering, strong on mobile | heavy throttling after connect | free |
| Tor Browser | almost every network block | networks that block Tor itself | free |
| Paid VPN | geo walls, SNI cuts, IP blocks | VPN protocol blocked or throttled | from a few $/month |
| Self-hosted VPN | everything, against your own exit | VPS providers blacklisted by sites | VPS cost |
| GoodbyeDPI / zapret | DPI packet tricks | whitelist-only censors | free, technical |
| Archive copies | any network block, dead pages | logins, dynamic content, paywalls | free |
| Translate proxy | simple fetches without any install | JavaScript-heavy sites, logins | free |
| Travel eSIM | the entire local network filter | data cost; not a fix for site-side geo | paid |
Encrypted DNS and resolver changes
If the diagnosis says DNS, stop here - this is all you need. Change the resolver to 8.8.8.8 (Google) or 1.1.1.1 (Cloudflare) [8], and prefer the encrypted variants: DoH wraps every lookup inside HTTPS so the network sees the query but not its content. We keep a per-platform setup guide for encrypted DNS [7].
ECH - hiding which site you visit
ECH encrypts the entire TLS ClientHello, so the censor's classic trick - reading the plaintext site name from the handshake and cutting exactly that connection - stops working on hosts that support it [2][6]. It is a browser setting, not an install, and it is the right fix when a site works over http:// but hangs on https://. Details and per-browser steps: ECH explained.
WARP, Psiphon, Lantern - free tunnels
Tunnels move both the handshake and the exit, so they beat connection-layer and IP-layer blocks at once. Cloudflare WARP is the lightest: one toggle, and your traffic rides Cloudflare's network with encrypted DNS included [7]. Psiphon is built for censorship specifically and is strongest on phones; Lantern is the other long-standing nonprofit option.
Tor Browser - the heavy answer
The Tor Browser routes your traffic over three volunteer relays, so no single hop sees both who you are and what you visit [9]. It defeats nearly every network-level block, and if the network blocks Tor itself, bridges get you in. It is slower than a VPN and some sites actively block its exits - use it for reading, research and anything sensitive. Setup and bridges: Tor Browser guide.
VPNs - paid or your own
A VPN fixes every network-side layer in one move and is the standard answer for geo walls. The market is full of affiliate-driven nonsense, so judge a VPN by its logging policy and jurisdiction, not its homepage: we keep an honest buying guide and an overview of the free tiers that are actually safe. EFF's Surveillance Self-Defense has its own checklist - it agrees the threat model matters more than the marketing [10].
If you control a server anyway, you can run your own WireGuard endpoint and become your own VPN operator: self-hosted VPN guide.
Packet tricks: GoodbyeDPI and zapret
In networks where censors use DPI appliances to cut connections mid-handshake, tools like GoodbyeDPI and zapret rearrange packets so the pattern matcher misses. They are free, tiny and legal to tinker with in most places, but they are expert tools - read the GoodbyeDPI and zapret guide before you trust one.
Zero-install: archives, translate proxy, onion sites
When you cannot install anything (school PC, work laptop, someone else's phone):
- Archived copies - the Wayback Machine serves the page it stored earlier; the network never sees the original site at all.
- Translate proxy - Google's translator fetches the page on its own servers and shows it to you inside its own interface. Our translate proxy guide has the exact URL pattern and the honest limits.
- Official onion sites - major operators (newsrooms, broadcasters, social platforms) publish official Tor onion addresses that bypass filtering entirely [9]. Use our official onion sites list - never an onion address from an unverified list.
The travel eSIM trick
A separate data eSIM runs on a different mobile network. That sidesteps hotel, campus and ISP filters completely, without any tool your network could object to. It costs data money and does nothing about site-side geo blocks, but as a clean escape hatch it is underrated: travel eSIM guide.
Traps that waste your time or steal your data
- "Free unblocker" websites and sketchy proxy extensions. You are sending all your traffic through a stranger. Enough said - the nonprofit and open-source options above are free too [10].
- Fake mirror domains. Search results are full of "mirror" copies of blocked sites built to harvest logins. Only use operator-published addresses and official onion URLs [9].
- Search-engine cache links. These are gone: Google removed cache links and the
cache:operator from search in 2024 [12]. Use a proper archive instead. - "Modded" or cracked app downloads. Tampered app bundles of blocked apps are a classic malware delivery route. Get the real app from the official store or project site [10].
- Trusting one symptom. A DNS block and an SNI cut look identical in a screenshot. Thirty seconds with the diagnosis routine above saves an hour of installing the wrong thing [1].
Staying safe and legal
Circumvention tools are legal to use in most countries, and using them to read is lawful nearly everywhere; but the law varies by country, some networks (schools, employers) have their own rules about what you may run, and a few states criminalize bypassing official filters. This guide is information, not legal advice - for the legal situation where you are, EFF's censorship hub [11] and organizations like Freedom House, whose Freedom on the Net reports document how restrictions keep expanding worldwide [13], are good starting points.
Two honest risk notes:
- Managed devices are logged. On a school or work machine, assume every connection attempt and every tool you install is recorded by the device administrator. Prefer zero-install methods there.
- Anonymity is not the same as access. A VPN gets you into the site; it does not make you anonymous against the VPN provider, the site or your OS. EFF's tool guide explains choosing tools by what you are actually protecting [10].
If it still does not work
Escalate in this order - each step tells you something:
- Re-run the diagnosis from a completely different network. If the site fails identically everywhere, the problem is the site, not the block.
- Test the site in OONI Probe and look it up in OONI Explorer [4] - the public measurement history often shows whether a block is new, total, or DNS-only. Our methodology page explains how we read these measurements.
- Switch method class, not method brand: if every resolver change fails, the block is not at the DNS layer - go straight to a tunnel.
- If tunnels fail too, the network is filtering the tunnel protocol itself: use Tor with bridges [9], or Psiphon's built-in obfuscation, or the GoodbyeDPI route if DPI is the mechanism.
- For site-side blocks (geo, age, account walls), nothing local helps: you need a legitimate exit in an allowed country - a VPN whose server location matches, or the operator's own official alternative (apps, onion sites, regional mirrors they publish themselves).
- Check our site pages for the specific site you are missing - we track the usual block type per site and per country, with the methods that beat it.
If you tell one story from this page: diagnose first. The layer decides the fix, and the symptom decides the layer [1].
FAQ
How do I know which type of block my network uses?
Read the symptom: block pages and failed name lookups mean a DNS block, a page that hangs only on HTTPS means a connection cut, nothing connecting at all means an IP block, and a site that loads but refuses your region is blocked on the site itself. OONI Probe tells you the same thing with measurement data.
Why does the site work on mobile data but not on my Wi-Fi?
Because the block lives on the network, not on the site. Your mobile carrier uses different resolvers and filters than your home, school or office network. The fix is whatever removes the interference on the failing network - most often encrypted DNS or a tunnel.
Is it legal to unblock a website?
Using circumvention tools is legal in most countries, but the law varies: some states restrict filters more aggressively, and school or workplace networks have their own rules. This page is information, not legal advice - check your local situation.
Does changing my DNS resolver actually work?
It works whenever the block is at the DNS layer, which is the most common casual block. It does nothing against SNI-based connection cuts, IP blocking or site-side geo walls - that is why the diagnosis step matters.
Are free web proxies safe to use?
Usually not: you send all your traffic, including logins, through an anonymous operator with unknown logging and no accountability. Prefer reputable free options - Cloudflare WARP, Psiphon, the Tor Browser - or EFF-vetted tools instead.
Can my school or employer see that I used a VPN or Tor?
They can usually see that you connected to a VPN or the Tor network, even when they cannot see what you did inside the tunnel. On managed devices, assume every connection attempt is logged. Zero-install methods such as archived copies avoid installing anything but still leave traces.
What happened to Google's cached page links?
Google removed cache links and the cache operator from search in 2024. To read a stored copy of a page, use an archive service such as the Wayback Machine instead.
Which method should I try first?
The cheapest one that matches your diagnosis: encrypted DNS for name filtering, WARP or ECH for connection cuts, a tunnel for IP blocks, and an exit in the right country for geo blocks. The five-minute routine at the top of this guide resolves most cases.