methods / self-hosted-vpn
Self-hosted VPN on a VPS: WireGuard setup guide
Short answer
Rent a VPS, install WireGuard, generate keys, and run a small server config with NAT forwarding plus a client config with AllowedIPs 0.0.0.0/0. Twenty minutes, a few dollars a month - with one exit IP that is yours and abuse mail that goes to you.
The most private VPN is the one whose operator you are: a small server (VPS) that you rent, a WireGuard tunnel from your devices to it, and an exit IP that belongs to exactly one person. No provider in the trust path, no shared exits, no "logging policy" to believe - the policy is that you do not even have the logging code running [1].
The trade-offs are equally real: you pay for the VPS, you get one fixed exit IP (which some sites classify as datacenter traffic), and any abuse complaint goes to you. This guide walks the setup honestly, at the level where it is copy-pasteable.
Why WireGuard
WireGuard is a modern VPN protocol designed for simplicity: a fraction of the code of OpenVPN, high performance, and a small, auditable crypto design [2]. It ships in the Linux kernel and in packages for every platform [1]. For a personal exit node it is the right default; if your censor hunts WireGuard handshakes, that is the obfuscation fight - see GoodbyeDPI and zapret or Amnezia, which packages WireGuard variants with obfuscation [6].
The setup, end to end
You need: a VPS (any small instance from a provider you accept jurisdiction-wise), a domain or its IP, and twenty minutes.
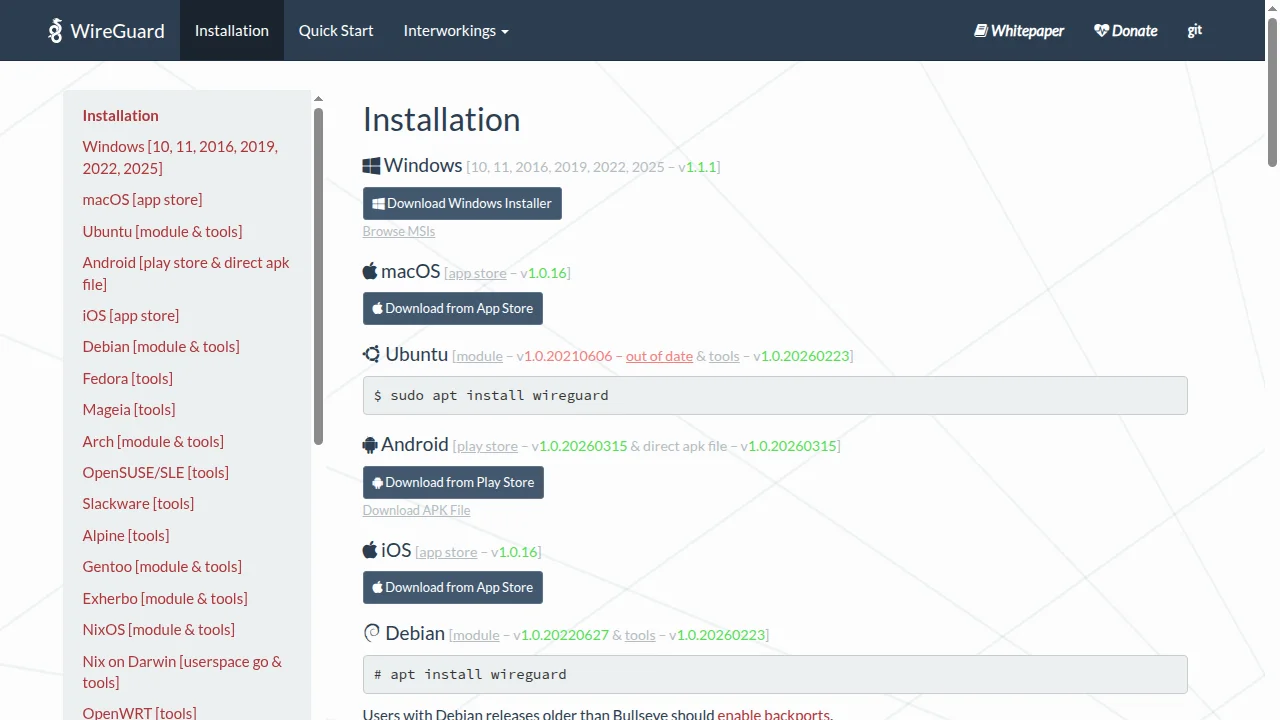
1. Install WireGuard on the server [1]:
sudo apt update && sudo apt install wireguard2. Generate the server keys:
cd /etc/wireguard
umask 077
wg genkey | tee server.key | wg pubkey > server.pub
3. Create /etc/wireguard/wg0.conf - replace 5.6.7.8 with your VPS IP and SERVER_PRIVATE_KEY with the contents of server.key:
[Interface]
Address = 10.66.66.1/24
ListenPort = 51820
PrivateKey = SERVER_PRIVATE_KEY
PostUp = iptables -A FORWARD -i wg0 -j ACCEPT; iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
PostDown = iptables -D FORWARD -i wg0 -j ACCEPT; iptables -t nat -D POSTROUTING -o eth0 -j MASQUERADE

[Peer]
PublicKey = CLIENT_PUBLIC_KEY
AllowedIPs = 10.66.66.2/32
4. Enable IP forwarding and start the tunnel:
echo "net.ipv4.ip_forward=1" | sudo tee /etc/sysctl.d/99-wg.conf
sudo sysctl --system
sudo systemctl enable --now wg-quick@wg0
5. Client config on your laptop/phone - the same tool generates keys on your device; replace CLIENT_PRIVATE_KEY, SERVER_PUBLIC_KEY, and the endpoint:
[Interface]
PrivateKey = CLIENT_PRIVATE_KEY
Address = 10.66.66.2/24
DNS = 9.9.9.9

[Peer]
PublicKey = SERVER_PUBLIC_KEY
Endpoint = 5.6.7.8:51820
AllowedIPs = 0.0.0.0/0, ::/0
PersistentKeepalive = 25
AllowedIPs = 0.0.0.0/0 sends all traffic through the tunnel; list only specific networks instead and only those routes use the VPS. Then activate: sudo wg-quick up wg0 on the client, or import the config into the official WireGuard apps on iOS, Android, Windows and macOS [1].
6. Verify. Check your exit address on the 1.1.1.1 help page - it should show the VPS provider's network, not yours.
Hardening the box
The VPS is now your network edge - treat it like it:
- SSH with keys only, no password logins; enable unattended security upgrades.
- The WireGuard port is silent to probes: unauthenticated packets get no handshake response, so port scanners see nothing interesting [2]. Do not add other services without reason.
- Keep the box small. A single-purpose server with a firewall list (allow SSH, WireGuard, nothing else) is a bad target.
- Log in as little as possible. The server should need no attention for months; that is the point.
If you want less handiwork, two respectable shortcuts: algo by Trail of Bits automates a security-reviewed personal VPN setup [3], and wg-easy adds a small web UI for managing several devices [4]. For team-style mesh networking rather than an exit node, Tailscale is a managed WireGuard overlay [5].
The honest trade-offs
- One exit IP. Convenient for stability; inconvenient for sites that treat datacenter IPs with suspicion, and useless against geo blocks that require many regions. Commercial VPNs exist partly for their spread of exits - judge both models with our VPN buying guide.
- You are the operator. Abuse mail (copyright, spam, attacks) forwarded by the VPS provider is yours to answer, and the provider can suspend you per its acceptable-use policy. Do nothing through your tunnel you would not do from home.
- Jurisdiction follows the VPS. Pick a country and provider the same way you would judge a commercial VPN's jurisdiction [7].
- It does not make you anonymous. The payment trail, the IP you configured it from and your account all point at you. This is about independence, not invisibility [7].
- No obfuscation by default. Plain WireGuard handshakes are recognizable to DPI. On hostile networks, add obfuscation layers (GoodbyeDPI family) or use tools built for that fight.
A legal note, plainly: running a personal VPN is legal in most places; forwarding traffic through it makes you responsible for what passes. This guide is information, not legal advice [7].
FAQ
Is a self-hosted VPN cheaper than a commercial one?
Usually yes for a single user: a small VPS costs a few dollars a month, while a decent paid VPN is similar or more - the saving is real but not dramatic. What you actually gain is control: one exit, no provider, your own logging policy (none).
Can I use my VPS VPN to unblock streaming?
Sometimes, but expect datacenter-IP blocking: streaming services classify VPS address ranges and often refuse them. That is a site-side decision no setup changes - the same wall our choosing-a-VPN guide describes.
Is WireGuard hard to maintain?
Almost not at all: the config does not drift, updates run through the package manager, and there is no state to lose. The maintenance burden is the server itself - security updates and the occasional reboot.
Does my own VPN make me anonymous?
No. The payment trail, the IP you configured it from and your account all identify you, and the VPS provider knows your traffic. Self-hosting is about independence and control, not invisibility - that is Tor's job.
What if my VPS IP gets blocked by a site?
You can move the exit: new instance, new IP, same keys. That is the hidden advantage over commercial providers - you are never stuck with one burned address.
Should I add obfuscation to my WireGuard tunnel?
Only if your network actively hunts WireGuard handshakes. Plain WireGuard is fine on normal networks; on hostile ones, obfuscated variants or the packet-trick tools are the escalation path.