methods / doh-setup
DNS over HTTPS: set up DoH in every browser
Short answer
Turn on secure DNS in your browser (Firefox: Max Protection, Chrome and Edge: Use secure DNS), or set it system-wide - Windows 11, Android Private DNS or a signed profile on iOS and macOS. Then verify on the 1.1.1.1 help page. DoH beats name-filtering blocks, not SNI or IP blocks.
If your diagnosis says the block is at the DNS layer - block pages, "server not found", or a site that loads on mobile data but not on your network - then encrypted DNS is the cleanest fix there is: a few settings, no extra software, and the filter loses its choke point entirely. DoH wraps every name lookup inside normal HTTPS traffic, so the network between you and the site can no longer read, rewrite or refuse your lookups [1].
This guide covers every way to turn it on - browser, Windows, Android, iOS, macOS, router - how to verify that it is actually working, and the honest limits: what DoH fixes and what it cannot.
Is a DNS block really what you have?
Thirty seconds, before you change anything. A DNS block is the most likely answer when the site shows an ISP block page, a search-engine error, or "DNS probe finished / server not found" while other sites load normally, and especially when the same site loads fine on mobile data. If instead the page hangs forever only on https://, or nothing to that address connects at all, the block is deeper than DNS - encrypted DNS will not help there. Our general unblock guide has the full symptom table.
The four DNS protocols, compared
"Encrypted DNS" is an umbrella over three different standards, and knowing which is which matters because each one is configured somewhere different:
| Protocol | Encryption | Port | Where you meet it |
|---|---|---|---|
| Do53 (plain DNS) | none | 53 | every default network |
| DoT | TLS | 853 | Android Private DNS, routers |
| DoH | HTTPS | 443 | Firefox, Chrome, Edge, Windows 11 |
| DoQ | QUIC (HTTP/3) | 443 | newer resolvers and servers |
The standards: DoH is RFC 8484 [1], DoT is RFC 7858 [2] and DoQ is RFC 9250 [3]. For unblocking, DoH is usually the right pick: it rides on port 443 next to your normal web traffic, so a network cannot quietly kill it without breaking the web itself - which is why browsers and Windows 11 standardized on it. DoT on port 853 is easy for a hostile network to spot and cut, which is a real weakness on filtered networks even though the content is encrypted [2].
Browser setup (works everywhere, five minutes)
The browser switch encrypts lookups for everything you do in that browser. It is the fastest route and survives OS limits.
Firefox
- Open Settings, search for "DNS over HTTPS", or go to Privacy & Security and find DNS over HTTPS.
- Set the status to Max Protection. The default "Default Protection" silently falls back to the system resolver when it fails - and a filtering network makes it fail on purpose [7].
- Pick a provider: Cloudflare (fast, minimal data retention) or Quad9 (blocks malware domains) [7].
- Restart the browser. Previously "not found" sites should now resolve.
Chrome and Edge
- Open
chrome://settings/security(in Edge: Settings, Privacy, search and services, Security). - Enable Use secure DNS.
- Pick a provider from the list, or choose "With:" and paste a custom DoH URL such as
https://dns.quad9.net/dns-queryorhttps://cloudflare-dns.com/dns-query[9]. - Restart the browser.
Safari
Safari uses whatever the operating system is set to - there is no in-browser switch. Set encrypted DNS system-wide (below) and Safari and every other app inherit it.
System-wide setup (every app, every browser)
The browser switch only protects that browser. The system switch protects everything - apps, mail clients, game consoles behind the same router - which is what you want once you know DNS is the problem.
Windows 11
Windows 11 has native DoH support [11]:
- Settings, Network and internet, Wi-Fi (or Ethernet), your connection, DNS server assignment, Edit.
- Switch from Automatic to Manual, turn on IPv4, and enter
1.1.1.1as preferred and1.0.0.1as alternate DNS server [4]. - Set DNS over HTTPS to "On (automatic template)".
- Repeat for IPv6 with
2606:4700:4700::1111and2606:4700:4700::1001.
On Windows Server (2022 and newer) the same feature is managed centrally through Group Policy or registry keys - relevant for anyone running a small office network [12].
Android
Android's "Private DNS" feature (Android 9 and newer) encrypts lookups for the whole phone. It is DoT rather than DoH [2], which means the lookups are encrypted but the dedicated port 853 can be blocked by serious filters - on casual networks it works perfectly:
- Settings, Network and internet, Private DNS (naming varies by vendor; search "Private DNS" in Settings).
- Choose "Private DNS provider hostname".
- Enter
one.one.one.one(Cloudflare) ordns.quad9.net(Quad9) [4][9]. - Save. Every app now resolves over TLS.
iOS and macOS
Apple devices take encrypted DNS as a configuration profile: a small signed file that carries a DNSSettings payload with a DoH server URL [10]. You do not write these by hand - Cloudflare and Quad9 publish signed profiles, and the easiest trusted route on iOS is the official 1.1.1.1 app from the App Store [4]. On macOS you can install the same profile system-wide (System Settings, Privacy & Security, Profiles).
Linux
There is still no single distro-wide DoH switch. The pragmatic setup on a desktop is the browser switch (above) plus a per-app check; system-wide, systemd-resolved supports DoT via DNSOverTLS=yes in /etc/systemd/resolved.conf, with DoH arriving through third-party resolvers. If you just need the site back, the browser switch covers the web.
Router setup (one switch, whole household)
Setting DoH or DoT on the router protects every device behind it, including TVs and consoles that have no settings of their own. Support varies by router firmware; Cloudflare and Quad9 keep device-by-device instructions including the common router brands [4][9]. Two honest caveats:
- A router-level setting changes which resolver you use, but older routers only support plain DNS forwarding - check that your firmware actually offers DoH/DoT before expecting encryption.
- If other people share the network, a household-wide filter change is something to do openly, not quietly.
Verify that it is working
Settings lie. Verify:
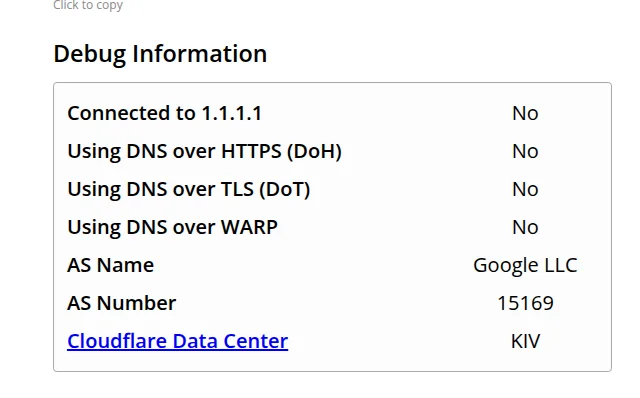
Open the 1.1.1.1 help page [5]. After a working browser DoH setup you will see "Using DNS over HTTPS (DoH): Yes". After Android Private DNS or a router DoT setup, "Using DNS over TLS (DoT)" flips to Yes. If both still say No, the setting did not stick - most often the browser was not restarted, or the OS change needs the network to reconnect.
As a second check, resolve the blocked domain in the dns.google web resolver [13]. If Google's resolver returns the site's address while your network's resolver refuses, you have proven a DNS block in thirty seconds.
When DoH is not enough
DoH removes name resolution as a choke point, and that is all. The block continues elsewhere if:
- The handshake is cut (SNI block). Your browser still announces the site name inside the TLS handshake, so a censor can cut the connection after your lookup succeeded [1]. The fix for that is ECH in the browser or a tunnel such as WARP.
- The IP is blocked. Packets to the server address are dropped regardless of DNS. Any tunnel with a different exit helps: Psiphon, the Tor Browser or a VPN.
- The site blocks you. Geo, age and account walls sit on the operator's side; no resolver setting changes them.
- The device is managed. School and work administrators can push enterprise policies that disable browser DoH, force lookups back to the company resolver, or kill automatic upgrades entirely by answering NXDOMAIN for Firefox's canary domain
use-application-dns.net[8]. If every provider fails on a managed device, that is what happened - and assume the attempts are logged. - The resolver itself is filtered. In heavier censorship environments, the resolver's IPs or its TLS handshake to port 853/443 can be blocked. Then you need tools built for exactly that fight: GoodbyeDPI and zapret, or the Tor Browser with bridges.
Choosing a provider
All three big general-purpose resolvers are run by companies with published policies and encrypted endpoints:
- Cloudflare 1.1.1.1 - fastest in most regions, no selling of personal data per their published commitments; setup docs for every device [4].
- Google Public DNS 8.8.8.8 - extremely reliable, full DoH endpoint documented publicly [6].
- Quad9 9.9.9.9 - a Swiss foundation that filters known malware domains; a sensible family-safe default [9].
Cloudflare's family variants (1.1.1.2 blocks malware, 1.1.1.3 adds adult-site filtering) are also worth knowing: not for unblocking, but for setting up other people's networks responsibly [4].
One trust note, plainly: DoH moves your name lookups from your ISP's resolver to the provider you pick. Both could log. Pick a provider whose policy you accept, and remember that DoH was never designed to hide who you are - only to encrypt the question "where is this site?" [1].
FAQ
What is the difference between DoH and DoT?
Both encrypt DNS lookups. DoT is DNS inside a TLS connection on port 853, while DoH is DNS inside normal HTTPS traffic on port 443. DoH is harder for a network to block separately, because it looks like regular web traffic - which is why browsers and Windows 11 default to it.
Does DoH hide the websites I visit?
No. It encrypts the name lookup only. Your network still sees which addresses you connect to, and the TLS handshake still names the site unless the site supports ECH. For real hiding you need ECH or a tunnel such as WARP, Psiphon, Tor or a VPN.
Which DoH provider should I pick?
Cloudflare 1.1.1.1 for speed, Google Public DNS for reliability, Quad9 9.9.9.9 if you also want malware filtering. All three publish their policies; the choice is about whose data handling you trust, because DoH moves your lookups from your ISP to that provider.
Is Android's Private DNS the same as DoH?
No - Android's Private DNS uses DoT, the TLS variant on port 853. It encrypts the same way, but serious filters can block port 853 as a whole, so on hostile networks the browser-based DoH switch is the more robust option.
Why does my school or office network ignore my DoH settings?
Managed devices get enterprise policies that can force the browser back to the system resolver or disable DoH entirely. Firefox's automatic upgrade can even be switched off remotely by answering NXDOMAIN for its canary domain. If every provider fails on a managed device, assume a deeper block and that your attempts are logged.
Does encrypted DNS slow down my connection?
Barely, in practice: the first lookup to a new resolver pays one TLS setup, and resolvers keep the rest of the lookup speed. Many users see the same or better overall performance than with their ISP resolver, which is often slower and sometimes intercepts queries for ads.
How do I check that DoH is actually working?
Open the 1.1.1.1 help page - it reports whether your current lookups use DoH, DoT or WARP. As a second check, resolve the blocked name on dns.google: if Google's resolver answers while your network refuses, the DNS block is proven.