methods / goodbyedpi-guide
GoodbyeDPI: beat DPI blocks on Windows, step by step
Short answer
GoodbyeDPI (Windows) and zapret2 (Linux, BSD, OpenWrt, Windows) confuse deep packet inspection with fragmentation, fake packets and TTL tricks - free, open source, no third-party servers. They fix DPI-based blocks on otherwise normal networks; they do not fix IP or geo blocks.
Some censors do not filter names or addresses - they read your traffic patterns. Deep packet inspection (DPI) appliances sit inline on the wire and match the shape of connections: this looks like a VPN handshake, cut it; this looks like a blocked site's traffic pattern, cut it. When that is the mechanism, encrypted DNS changes nothing and tunnels get recognized and killed. The answer at that layer is more subtle: confuse the inspector at the packet level, so its pattern matcher never sees a clean target [1][5].
GoodbyeDPI (Windows) and zapret2 (Linux, BSD, OpenWrt and Windows) are free, open-source tools that do exactly this. They require no third-party servers, run only on your own machine or router, and fix a specific class of block. This guide explains what they do, the setup, and when to leave them alone.
What DPI can and cannot see
An inline DPI box reads every packet, matches connections against signatures, and intervenes by sending forged resets or dropping packets [5]. Two facts open a hole in that model:
- The censor's view of a connection can differ from the server's. A tool can send the censor a packet it will happily read - and make sure that packet never reaches the real server.
- Pattern matching is fragile. If the handshake arrives fragmented, with overlapping sequence numbers, or with fakes mixed in, the matcher misreads and lets the connection through [1][2].
Both tools use these exact strategies. zapret2's documentation reads like a small textbook: fake packets, TCP segmentation, sequence-number overlap, IP_ID manipulation, IPv6-specific modes, duplicates and combinations [2]. GoodbyeDPI applies the same ideas on Windows, and additionally handles passive DPI - boxes on an optical splitter that answer faster than the real server - by dropping their forged responses [1].
GoodbyeDPI on Windows
GoodbyeDPI is a single executable with a set of batch scripts; the project has 28.8k stars and is Apache-2.0 licensed [1]:
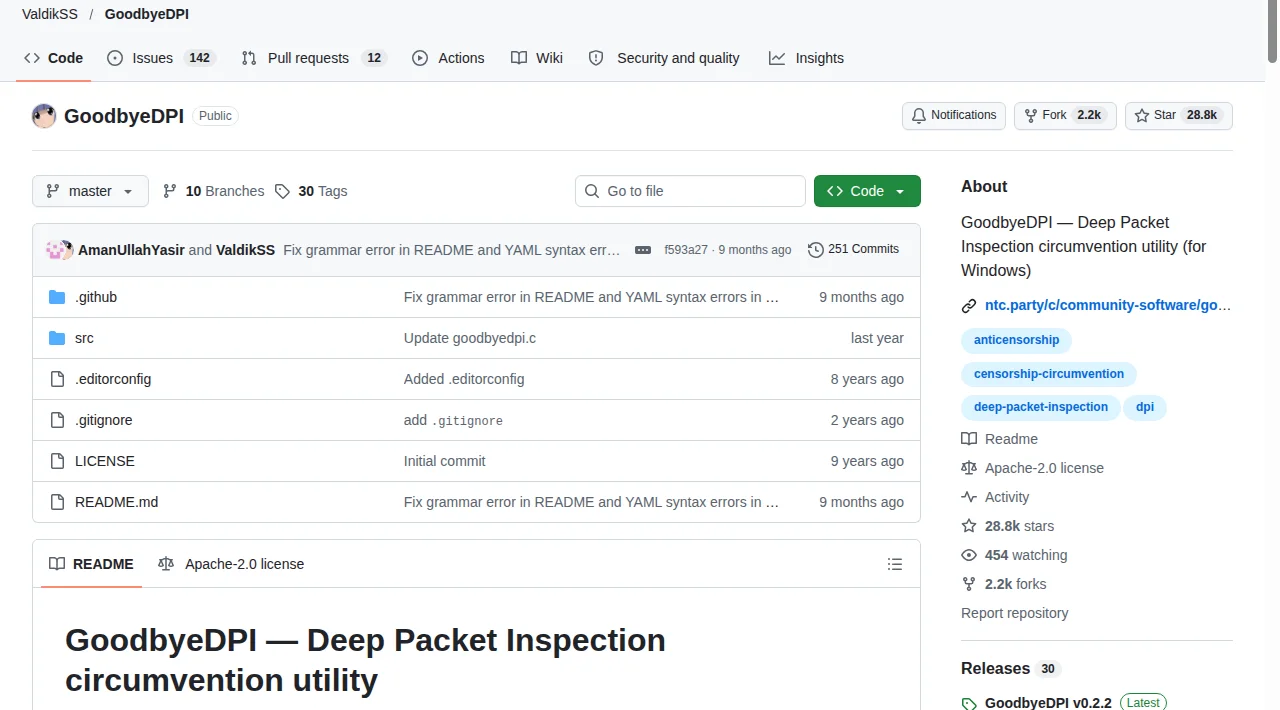
- Download the latest release only from the official Releases page [1]. Anything else - "GoodbyeDPI download sites", bundled installers - is a scam or malware.
- Unpack, and run the matching script as administrator (Windows 7 through 11, admin rights required) [1]:
- for Russia-style blocklists:
1_russia_blacklist_dnsredir.cmd - for other countries:
2_any_country_dnsredir.cmd
- The scripts launch GoodbyeDPI in the recommended mode and also redirect DNS to a non-standard port so poisoned answers never arrive [1].
Under the hood it loads the WinDivert driver, which uses the Windows Filtering Platform to redirect packets into the tool's userspace handler - it runs while the console window is open and stops when you close it [1]. For a permanent setup, the project explains how to run it as a Windows service.
One honest warning from the README culture around these tools: antivirus software occasionally flags the WinDivert driver, and zapret's maintainer explicitly warns that anyone pressuring you to download zapret from anywhere but the official repository is running a scam [2][3]. Verify the source every time.
zapret2 on Linux, BSD, OpenWrt - and Windows
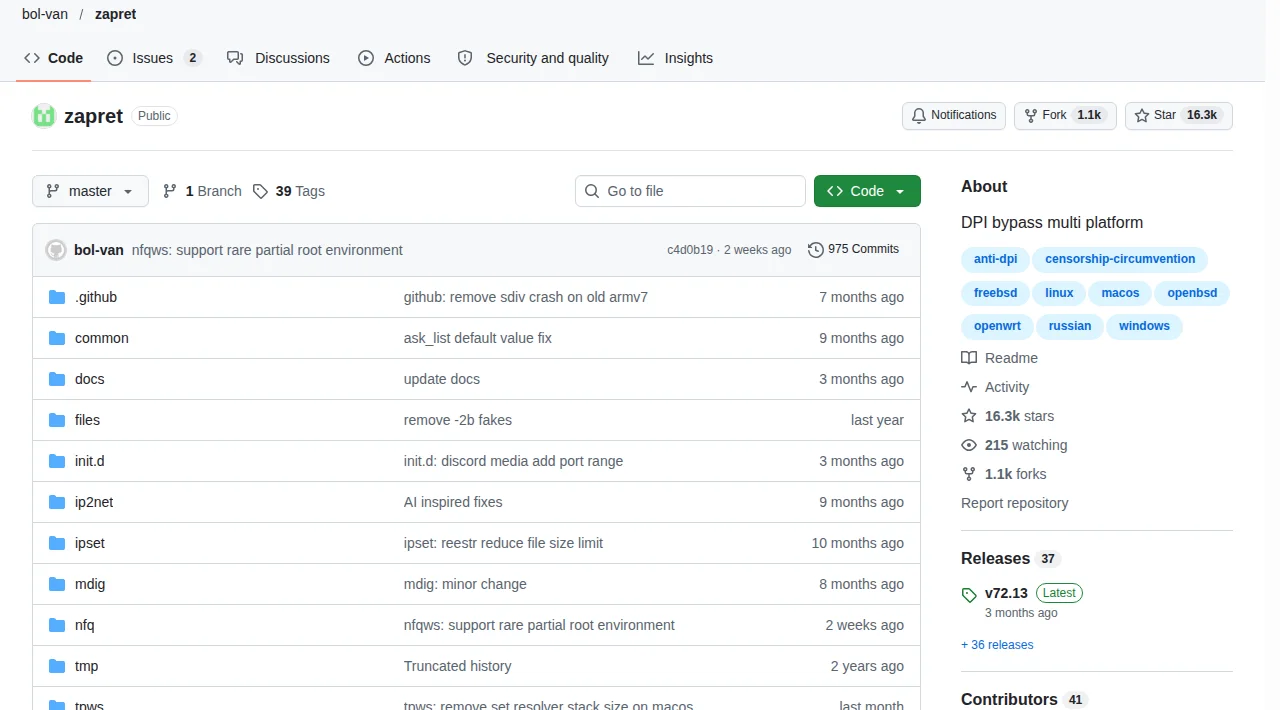
The original zapret (v1) is end-of-life; its successor zapret2 is the maintained version [2][3]. It is a standalone DPI countermeasure that needs no external servers, aimed primarily at low-power routers running OpenWrt, and it supports traditional Linux (iptables/nftables), FreeBSD and OpenBSD (ipfw/pf), and Windows (WinDivert). macOS is not supported [2].
- Get it only from the official repository [2].
- On Linux, start with the documented nftables rules that steer the first packets of connections on TCP 80/443 and UDP 443 into the NFQUEUE handler [2].
- Pick a strategy (fake, segmentation, TTL) per the manual and test against your block; strategies are combinations, and the right one is the one that survives your censor [2].
- On Windows, many readers use the popular community bundle zapret-discord-youtube - widely used, but a third-party packaging; the official zapret2 is the source of truth [4].
This is the expert tier of unblocking. Expect to read, experiment and re-test - and keep notes of what worked, because censors tune their filters over time.
When packet tricks are the wrong tool
- The block is at the DNS layer. A resolver change or encrypted DNS fixes it in minutes; packet tricks are overkill.
- The block is at the IP layer or on the site. No handshake trick moves your exit. That is WARP, Psiphon, Tor or a VPN territory.
- You want zero tinkering. These tools are command-line experts' tools. WARP is one toggle; Psiphon is one install.
- You are on a managed device. Loading a packet-manipulation driver on a school or work computer is visible to its administrators and likely against their rules.
A legal note, plainly: circumvention is legal in most jurisdictions, but network-level tinkering has its own rules on some networks and in some states. This guide is information, not legal advice - and EFF's threat-model guide is the right frame for deciding what you actually need [7].
Measure before and after with OONI Probe [6] - it tells you whether your block is DPI-flavored at all, which is the whole question these tools answer.
FAQ
What is deep packet inspection?
Censorship equipment that reads the content and shape of your connections instead of just names or addresses, matches them against signatures, and cuts what it recognizes - commonly used against VPNs and specific sites.
Why would packet tricks work when a VPN is blocked?
Because a VPN presents a recognizable handshake, while fragmentation, fake packets and TTL tricks make the handshake unreadable or untrustworthy to the filter. The censor drops nothing and the real server gets the intact connection.
Are GoodbyeDPI and zapret safe?
They are open source and widely audited by their communities, but they install a packet-manipulation driver and need administrator or root rights. Only download from the official repositories - both maintainers explicitly warn about fake download sites.
My antivirus flags GoodbyeDPI. Is it malware?
The WinDivert driver behaves in ways antivirus heuristics distrust, and false positives are common and documented. Verify you downloaded it from the official repository, and make your own call - or use a different tool if the warning bothers you.
Which one should I use - GoodbyeDPI or zapret2?
GoodbyeDPI is Windows-only and click-to-run. zapret2 covers Linux, BSD, OpenWrt routers and Windows with far more strategies, but expects command-line skills. On Windows, start with GoodbyeDPI; on routers and Linux, zapret2.
Can these tools get blocked or stop working?
Yes, permanently. It is an arms race: censors tune their filters, maintainers respond. Expect to update, change strategies, and occasionally switch tools entirely.
Do I still need encrypted DNS with these tools?
Usually yes. GoodbyeDPI's recommended scripts redirect DNS to a non-standard port to dodge poisoning, and zapret2 documents similar handling - name filtering is one more layer the censor may still control otherwise.