methods / ech-explained
ECH explained: hide the site name from your ISP
Short answer
ECH encrypts the TLS ClientHello, so the network can no longer read which site you are connecting to. It works when a browser with ECH, encrypted DNS and an ECH-supporting host come together - then name-based filtering simply stops. Geo blocks and IP blocks are untouched.
Every HTTPS connection starts with a handshake, and for most of the internet's history that handshake leaked the one thing a censor cares about: the name of the site you are visiting. The field is called SNI - Server Name Indication - and it travels in plaintext so busy servers hosting thousands of sites can pick the right certificate. Filtering networks read it and cut exactly the blocked domains, which is why a page can hang forever on https:// while http:// still loads [1].
ECH - Encrypted Client Hello - encrypts that handshake, hiding the site name inside public-looking traffic [1][2]. It is a browser setting plus a compatible host, it costs nothing, and where it works, name-based SNI filtering simply stops. This guide explains what ECH does, how to turn it on, and - honestly - when it does nothing at all.
How ECH hides the site name
The TLS 1.3 handshake sends a ClientHello message before any encryption exists. ECH splits that message in two [1]:
- a ClientHelloOuter, visible to the network, carrying only a harmless public name - usually the host's provider domain - and
- an encrypted ClientHelloInner with the real site name and settings, locked to a public key the site publishes in its DNS records.
The censor sees a normal-looking handshake for a provider like Cloudflare and cannot tell which of the millions of sites behind it you actually meant [1][2]. The design even survives stale keys: if decryption fails, the connection retries with fresh keys instead of dying [1][2].
The three conditions
ECH is a cooperation between your browser, your DNS and the site's host. All three must line up:
- A browser with ECH support. Firefox and Chrome ship ECH enabled; Edge inherits Chrome's behavior, other Chromium browsers vary. Test your current browser below.
- Encrypted DNS (DoH) switched on. The ECH public keys arrive inside HTTPS-type DNS records, and the browser must fetch them over DoH for them to survive tampering [1][3]. Our DoH setup guide covers every platform.
- A site whose host supports ECH. The host publishes the ECH config for the site. Large hosts (Cloudflare among the first) do this for their customers; small self-hosted servers usually do not [1].
Turn it on and verify
Firefox
- Settings, Privacy & Security, find DNS over HTTPS, set it to Max Protection with a real provider - ECH keys must arrive over encrypted DNS [3].
- ECH ships enabled by default in recent Firefox; to be sure, open
about:configand check thatnetwork.dns.echconfig.enabledandnetwork.dns.http3_echconfig.enabledaretrue[3]. - Restart the browser.
Chrome and Edge
- Open
chrome://settings/security, enable Use secure DNS, and pick a provider (same reason as above: the keys ride on DNS) [1]. - ECH is active in current Chrome by default - the flag
chrome://flags/#encrypted-client-helloexists for older versions. - Restart the browser.
Verify for real
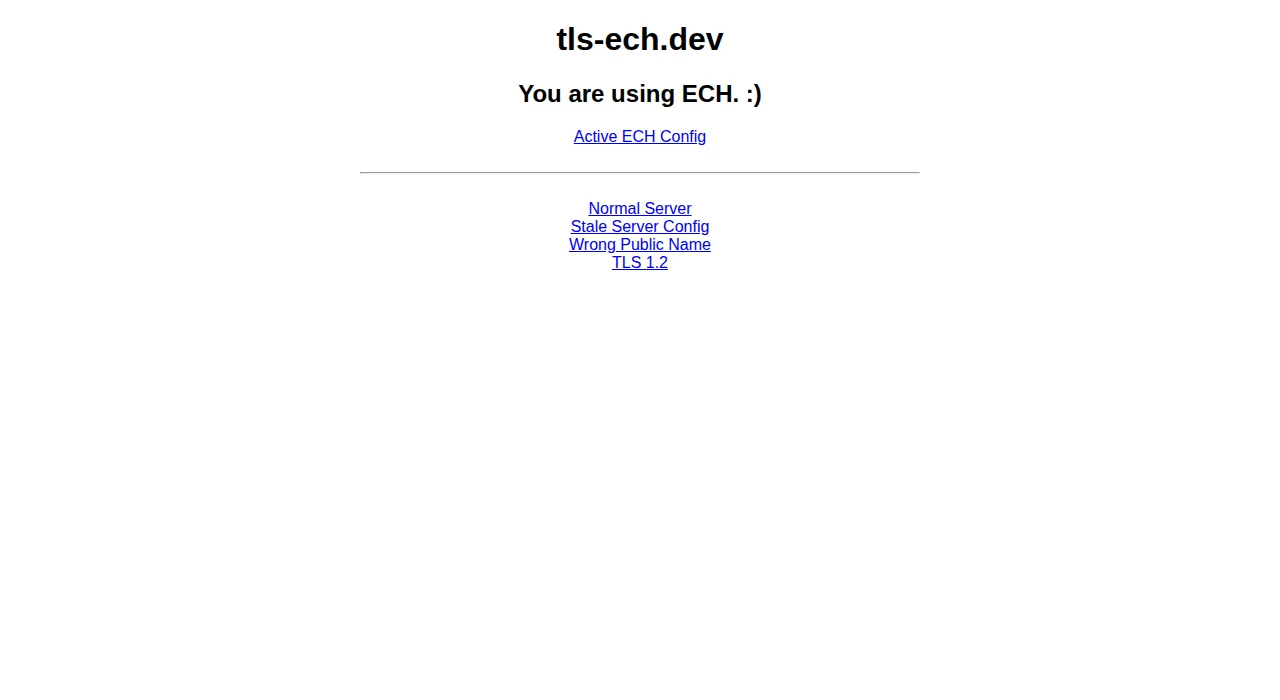
Open tls-ech.dev [4]. It answers plainly: "You are using ECH" or "You are not using ECH". Keep two tabs open - one on the ECH test, one on the blocked site - so you can see exactly when the protection is live. defo.ie hosts additional ECH test endpoints [6].
When ECH helps - and when it does nothing
ECH is a scalpel, not a hammer. It beats one specific kind of block: filtering that reads the TLS handshake. Measure first with the symptom table in our general unblock guide or OONI Probe [5], and check this list before blaming ECH:
- The site does not support ECH. Most of the web is not behind an ECH host; then the handshake is plaintext no matter what your browser does. Check by opening a known-ECH site on the same network: if that works and yours does not, your block is not SNI-based.
- The block is at the IP layer. Packets to the server are dropped regardless of handshakes. You need a tunnel: WARP, Psiphon or the Tor Browser.
- The block is on the site itself. Geo and account walls live after the handshake.
- The censor strikes back. Blocking ECH is the obvious counter-move - a network can filter the DNS records that carry the ECH keys or cut handshakes that offer ECH. If ECH worked yesterday and stalls today, that is what happened; move to a tunnel and its obfuscation, and re-test later.
ECH also pairs beautifully with the lighter tools: encrypted DNS plus ECH is the whole "stealth setup" on a machine where you cannot install anything, and it is the first thing to try before the heavier tunnels [7].
FAQ
What is the difference between ECH and DoH?
DoH encrypts your DNS lookups - the question 'where is this site?'. ECH encrypts the TLS handshake - the moment you announce which site you are connecting to. You need both: the ECH keys arrive through encrypted DNS, and together they remove the site name from every visible step.
Does ECH work for every website?
No. The site's host must publish ECH configuration in its DNS records. Large hosts do this for their customers; many self-hosted and smaller sites do not. If the site never offers ECH, your browser falls back to a normal handshake.
Can a censor block ECH?
Yes - by filtering the DNS records that carry the ECH keys, or by refusing handshakes that use it. ECH is strong where it is supported, but it is not censorship-proof; tunnels with obfuscation remain the heavier answer.
Does ECH hide my traffic from my ISP?
It hides the site name, not the traffic. Your ISP still sees the address you connect to and can still measure how much you transfer. Against IP-level blocking, only a tunnel with a different exit helps.
Why is my browser not using ECH even though it supports it?
The most common cause is encrypted DNS being off - the ECH keys arrive in DNS records, so without DoH the browser cannot learn them. Second most common: the site does not support ECH. Test with tls-ech.dev to separate the two.
Does ECH slow my connection down?
The encryption itself is negligible; the handshake carries a small extra payload. In practice you will not notice it. The visible difference is that name-based interference stops.